AI Governance & Control
Keep control as AI takes on more work.
We implement controls over what AI can access, which actions it can perform and when a person must approve.
Discuss your AI controlsIn your premises or organisation-managed cloud environment.
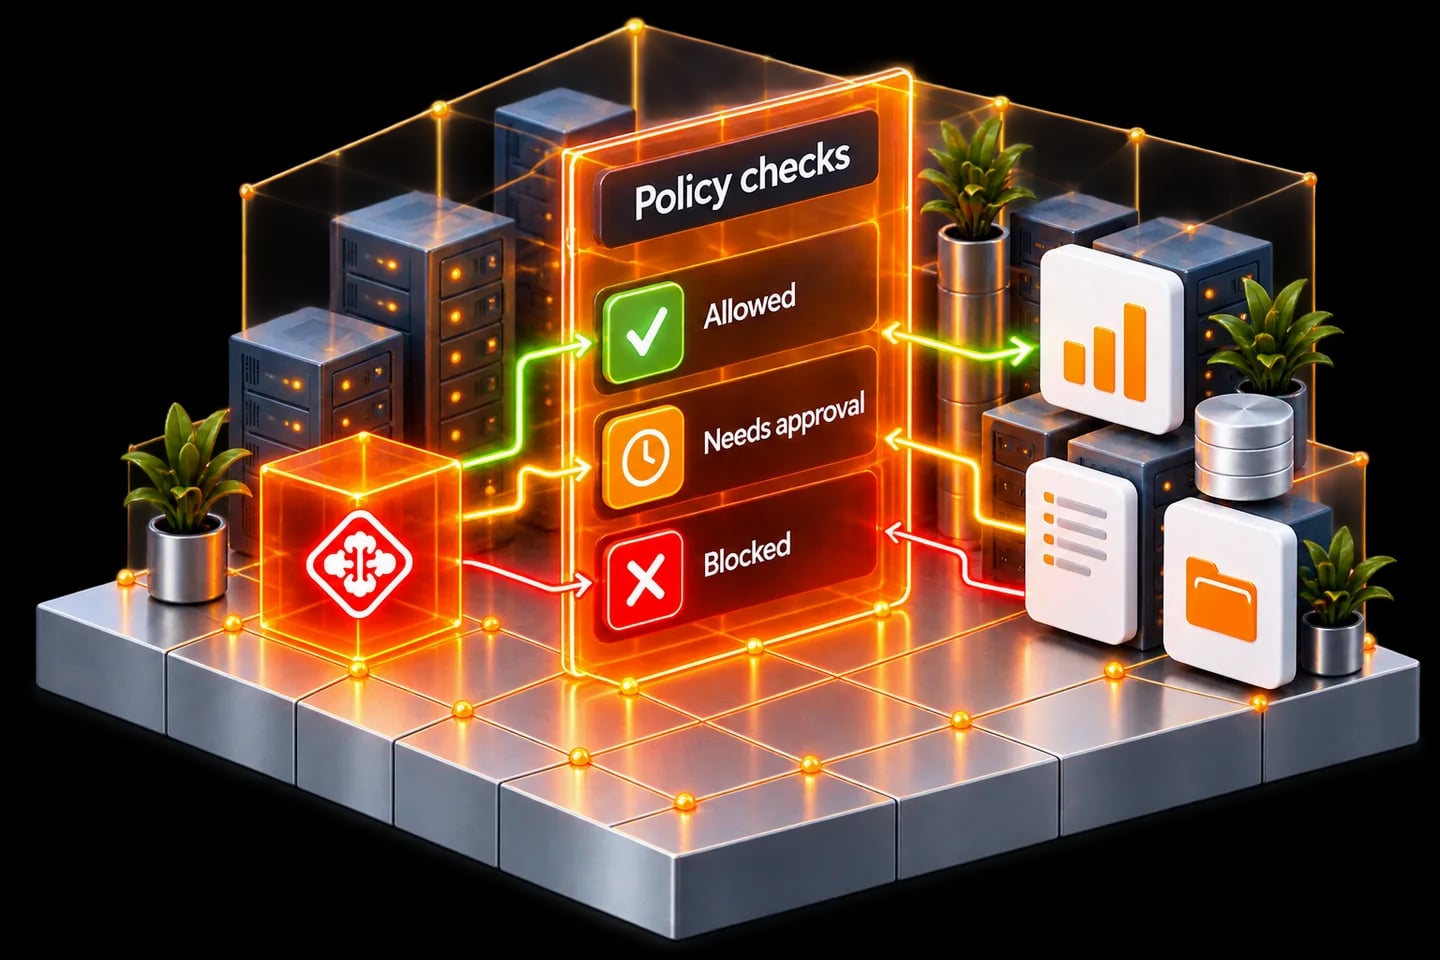
Clear answers before AI acts.
- 01
Who can access this information?
Agree permitted sources and roles.
- 02
What can the agent change?
Define the allowed actions.
- 03
Who approved that action?
Keep approval outcomes visible.
Translate your operating rules into controls your systems can apply.
Built around your operations
Controls that operate with the workflow.
Permissions, policy checks, approvals and visibility, designed together.
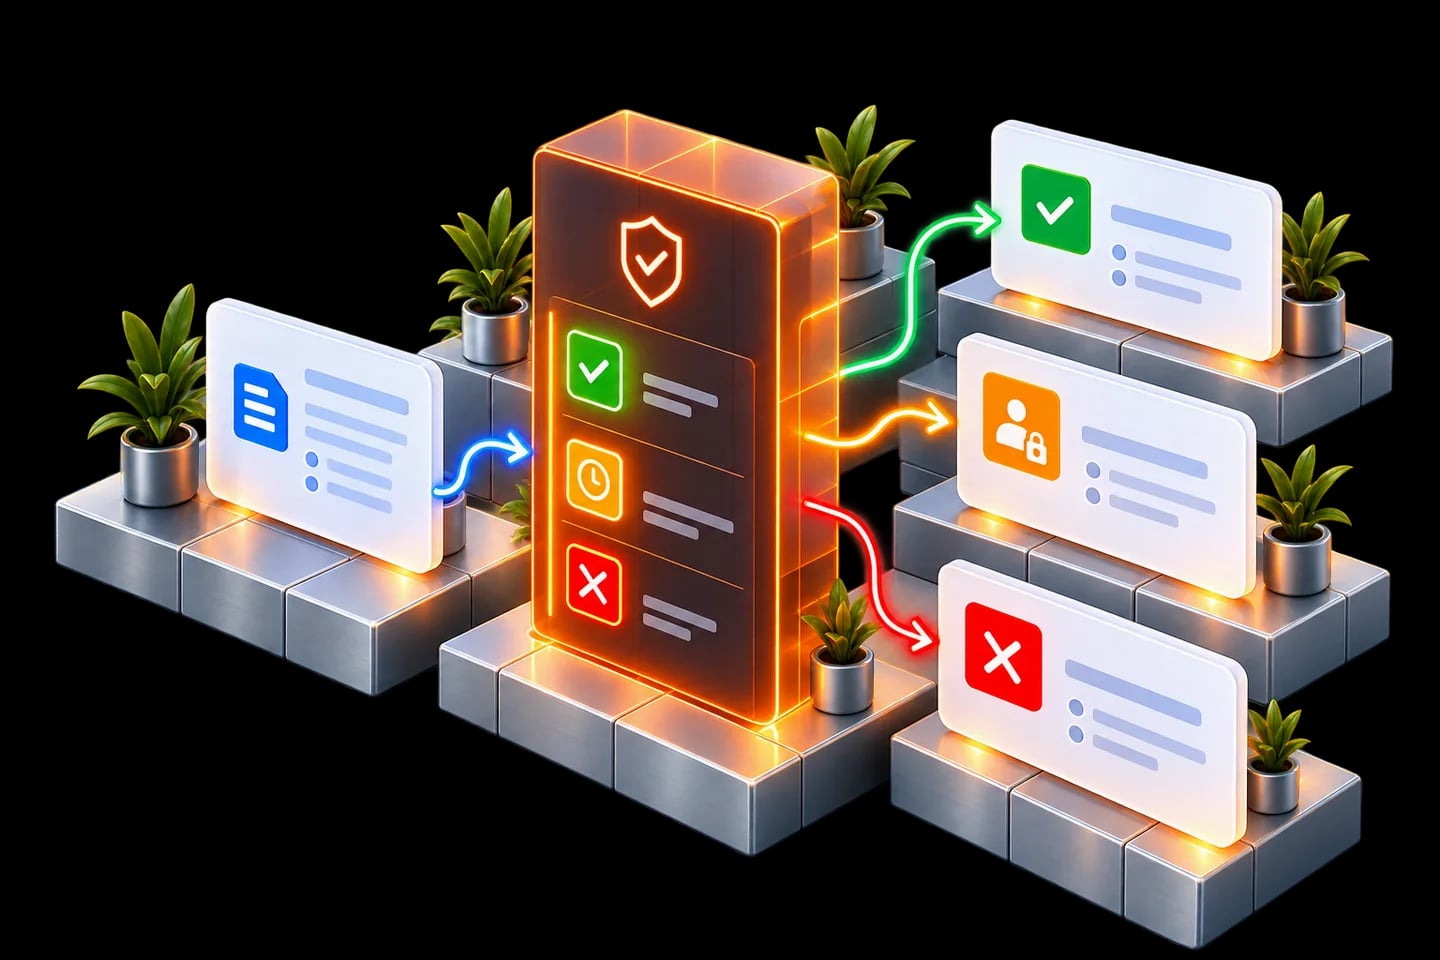
Access & permissions
Define which information and tools each user or agent may use.
Runtime policy enforcement
Enforce rules in software at supported data, tool and action boundaries.
Human approvals
Require review before important actions can proceed.
Activity monitoring
Record requests, actions and approval outcomes, with defined access and retention.
Define what AI may do before it acts.
Example: a configured set of permissions for one finance assistant.
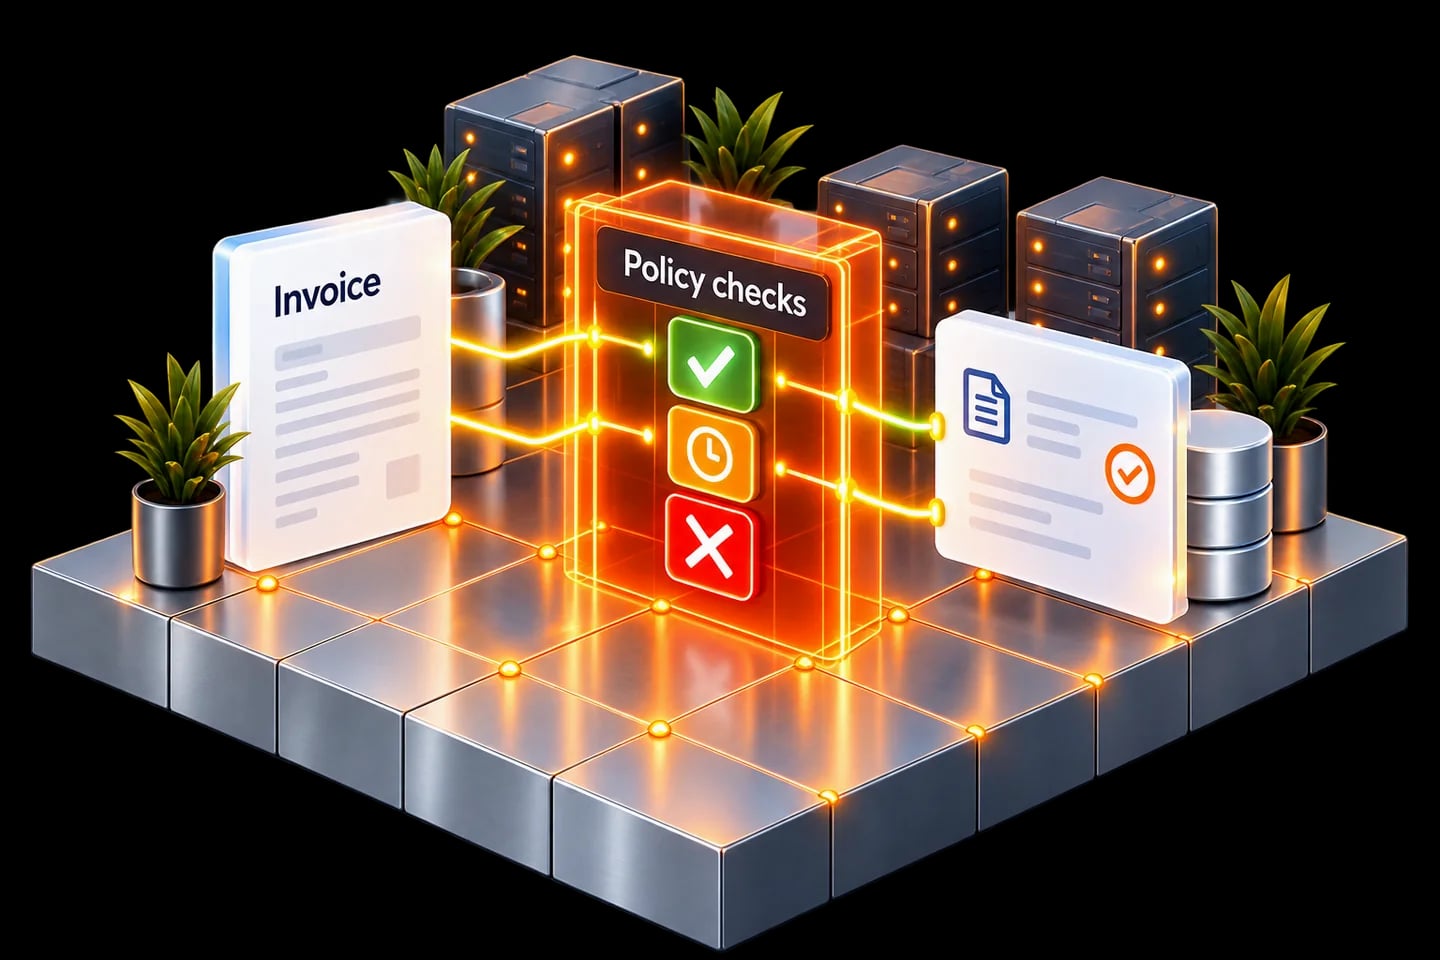
Read permitted invoice fields
ALLOWEDPrepare a draft entry
ALLOWEDSend information outside
BLOCKEDChange a financial record
APPROVAL REQUIREDExample permissions are configured to the workflow and organisation.
A workflow we can build
Your rules. Working controls.
We integrate controls with your existing identities, applications and infrastructure.
- 1
Your systems
- 2
Configure rules
- 3
Policy checks
- 4
Test allowed & blocked paths
- 5
Activity records
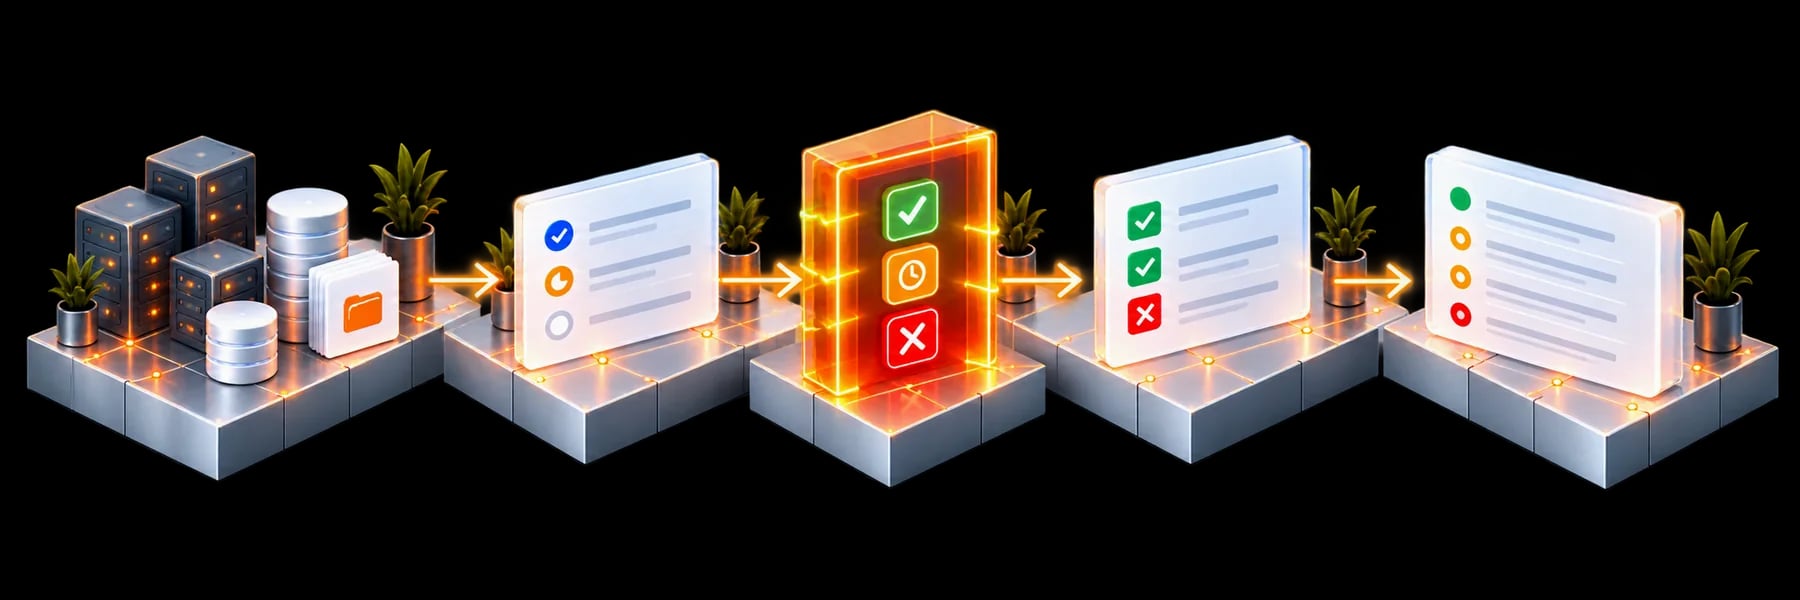
An engineering and integration service, tailored to supported enforcement points.
Delivery
Put controls into everyday work.
- 01
Map the rules
Define allowed data, tools and actions.
- 02
Implement controls
Connect permissions, policies and approvals.
- 03
Test the paths
Check permitted and denied behaviour.
- 04
Monitor & improve
Review activity and refine controls.
Start with a useful scope and agreed success measures. Test before expanding.
A few practical questions.
Does this guarantee correct AI answers?
No. Output evaluation and human review remain important. Governance defines access and action boundaries; it does not establish that every answer is correct.
Can this work with existing AI tools?
We assess the integrations and enforcement points supported by those tools before agreeing the scope.
Where do activity records stay?
In the agreed organisational environment, with defined access and retention.
Are instructions in a prompt enough?
Important boundaries need controls implemented in software at supported integration points, alongside clear operating procedures.